Dropzone AI: agents that investigate cybersecurity alerts
Dropzone AI connects agents to security tools to investigate alerts and gather evidence. Explore its approach and what to consider when evaluating it.
Voices depend on your browser and device; some require internet access. Code blocks are not read aloud.
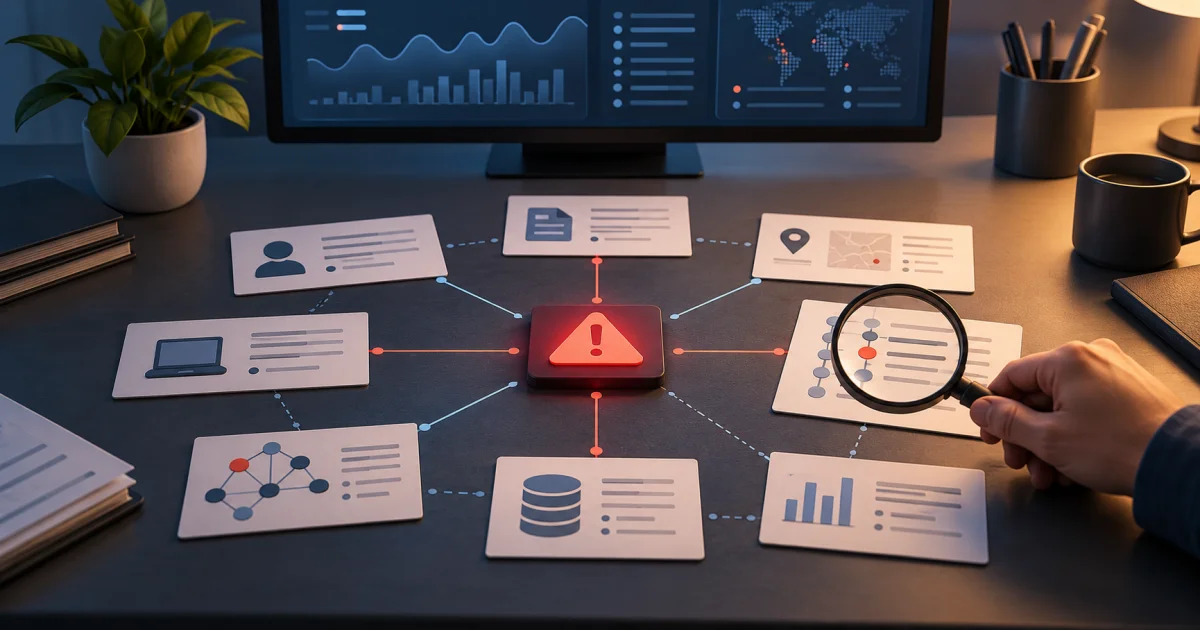
An alert on a screen does not tell the whole story. Unusual activity could be a threat, an authorized change, or simply something the tool did not recognize. Finding out which of these situations occurred requires gathering information.
Dropzone AI works on this investigation process. It offers agents for security teams, including alert analysis, threat hunting, and organizing information about risks relevant to the environment.
What does an AI SOC Analyst do?
SOC stands for security operations center: the team or structure that monitors events and responds to possible incidents. Dropzone's AI SOC Analyst is presented as an agent that investigates alerts using the tools connected to the operation.
The platform gathers context, consults information, and produces findings to support assessment. It also records the stages of the investigation and allows analysts to ask follow-up questions.
In simple terms, the idea is to help move from the initial warning to an explanation supported by evidence. This includes investigating whether a signal really indicates danger or is a false positive, the term for an alert that turns out not to represent the suspected threat.
An illustrative situation
Think of a team that receives a warning about unusual activity on a corporate account. The first task is to understand the context: was there an approved change? Do the logs show other related signals? Is there enough information to reach any conclusion?
An investigation agent can organize queries to permitted sources and present what it found. The team uses this material to decide how to proceed. The example is illustrative; the available checks depend on the connected systems and the scope defined by the organization.
What makes the approach interesting?
Dropzone highlights the ability to configure investigation strategies and maintain context about the environment. This matters because normal behavior in one organization may differ from that in another.
In my view, the most interesting point is making investigations more consistent and easier to review. A conclusion accompanied by records makes it possible to discuss whether the data justifies that result and identify what still needs to be checked.
How to evaluate without losing context
A good start is to compare the analyses with cases the team already knows. Observe the quality of the evidence, how incomplete information is handled, and the effort required to correct mistaken conclusions.
The company also describes containment actions on the platform. It therefore makes sense to define separately what the agent can consult and which responses it can execute, with clear ownership and approvals. The demonstration should reflect the actual operation: connected sources, permissions, and decision criteria are as much a part of the result as the AI.
Official information accessed on 21/10/2026.