depthfirst: AI for investigating security flaws in code
depthfirst uses AI agents to analyze code, investigate vulnerabilities, and propose fixes. Explore its approach and the criteria for evaluating it.
Voices depend on your browser and device; some require internet access. Code blocks are not read aloud.
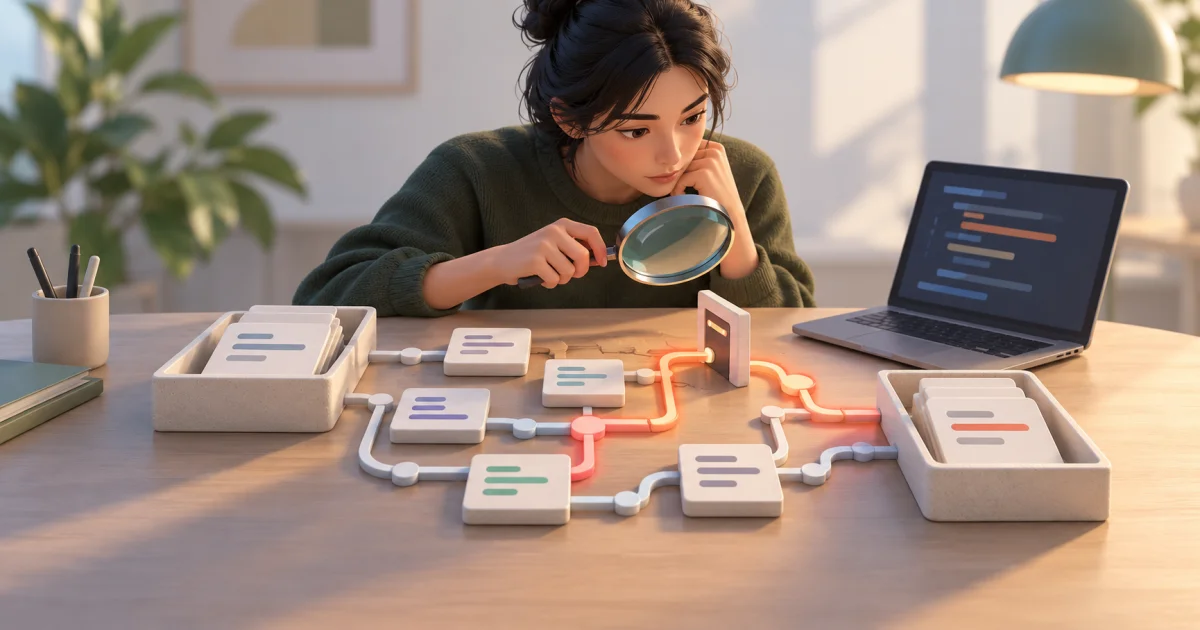
A system can pass the most obvious tests and still leave an important question unanswered: can each person access only what they should? For software developers, this kind of detail deserves attention before a new version reaches users.
depthfirst uses AI agents to investigate security risks throughout development. Its platform brings together code analysis and other areas of protection, aiming to follow the application's context through to execution.
Looking at how the system works
On its code security page, the company describes analyses of business logic, the path data takes, and the relationships between services.
Let's put that into plain language: a problem may depend on a combination of several parts of the program. Understanding the intended rule and what the code actually does helps assess where a flaw exists.
depthfirst presents checks of the project and proposed changes, along with evidence for its findings and suggested fixes. These suggestions can appear in the code review process, where developers assess changes before incorporating them.
A scenario to understand its usefulness
Imagine, as an illustration, an application used by different companies. Each customer should see only their own documents. During a change, the team wants to check whether this separation still works.
A security analysis can help locate sections related to permissions and point out a condition that deserves investigation. Those responsible then check the behavior and assess the proposed fix in an authorized environment.
The value of this work lies in the quality of the evidence: the problem, its relevance, and the effects of the suggested solution need to be understood.
Why this approach stands out
The idea of bringing security investigation closer to the development workflow is interesting because it makes the path from discovering a problem to addressing it more direct. The product page specifically describes delivering context and fixes alongside reviews.
My expectation for a tool like this would be to reduce the time needed to understand findings. A huge list of warnings does little to help when no one can distinguish what needs action.
How to evaluate it with the team
An initial test can use an authorized project and a known set of problems. It is worth observing whether the tool explains its findings, recognizes the application's context, and suggests changes that preserve the expected behavior.
The team should also define who reviews fixes, which repositories are in scope, and how to measure incorrect alerts. The current platform includes features beyond code; it makes sense to identify which ones fit the actual need. To start the conversation, the official website and product description offer a clear overview of the approach.
Official information accessed on 21/10/2026.